Category: AI Governance

AI risk management, compliance, and policy enforcement

  • AI Risk Heatmap: Matching Governance to Business Value

    AI Risk Heatmap: Matching Governance to Business Value

    In early 2024, Deloitte Australia made headlines for all the wrong reasons. An AI-generated government report contained fabricated information—statistics that looked credible but simply didn’t exist. The result: public criticism, a contract refund, and lasting reputational damage. It’s the kind of incident that keeps CISOs up at night, but here’s what makes it instructive: the same organization might have dozens of lower-risk AI tools running perfectly fine. The mistake wasn’t using AI—it was applying insufficient governance to a high-stakes use case.

    This is the fundamental challenge facing every enterprise today. Not all AI use cases carry equal risk. A customer service chatbot with access to PII is fundamentally different from an internal knowledge assistant. Yet many organizations apply the same governance to both—either over-governing low-risk use cases (killing innovation) or under-governing high-risk ones (creating liability).

    The numbers tell the story. According to Gartner’s 2025 research, organizations that conduct regular AI system assessments are three times more likely to report high business value from their generative AI investments. The governance isn’t just about risk avoidance—it’s about unlocking value. But the key insight from that same research is that governance must be proportional. Over-engineer controls for a low-risk internal tool, and you’ll strangle the innovation that makes AI valuable in the first place.

    The solution is risk-proportional governance: matching controls to the actual risk profile of each AI deployment.

    The AI Risk Heatmap

    Think of your AI portfolio like a financial investment portfolio. You wouldn’t apply the same due diligence to a Treasury bond as you would to a speculative startup investment. The same logic applies to AI governance. Plot your AI use cases on two dimensions: business value (how important is this use case to revenue, efficiency, or strategic goals?) and risk sensitivity (what’s the potential for harm—to customers, compliance, reputation, or operations?).

    This creates four quadrants, each demanding a different governance approach. Let’s walk through each one with specific guidance on what controls to apply—and equally important, what controls you can skip.

    Quadrant 1: High Value, High Risk (Govern Tightly)

    These use cases demand robust governance. The stakes are high on both sides, and this is where incidents like Deloitte’s tend to occur. According to a Harvard Law School analysis, 72% of S&P 500 companies now disclose at least one material AI risk—up from just 12% in 2023. The enterprises taking AI seriously are the ones getting governance right for high-stakes use cases.

    Think of customer support agents with PII access, financial data analysis agents, contract review and drafting systems, and HR policy chatbots. These are the applications where a single mistake can mean regulatory penalties, lawsuits, or front-page news. The risks are significant: customer-facing AI can leak sensitive data or violate privacy regulations like GDPR and CCPA. Prompt injection attacks can manipulate agent behavior. And if an AI agent gives incorrect legal or financial advice, the liability falls on your organization—not the AI vendor.

    For these high-stakes use cases, you need the full governance toolkit. Role-based access control ensures only authorized personnel can interact with sensitive functions. PII detection and masking prevents accidental data exposure. Comprehensive audit logging creates the paper trail regulators and auditors will demand. Human-in-the-loop review catches mistakes before they reach customers. Regular security testing identifies vulnerabilities before attackers do. And compliance reviews before deployment ensure you’re not creating regulatory exposure from day one.

    Quadrant 2: High Value, Medium Risk (Govern Moderately)

    Important use cases with manageable risk. Balance controls with usability—this is where most of your productive AI tools will live. Code assistants and copilots, sales research assistants, and AI meeting note takers fall into this category.

    The risks here are real but contained. Your code assistant might inadvertently train on proprietary code, leaking intellectual property to the model provider. Meeting transcription tools raise consent and privacy concerns. Sales assistants might expose competitive intelligence if prompts or outputs are stored insecurely. Third-party data processing adds vendor risk to your compliance surface.

    Moderate governance means being smart about where you invest control effort. Zero data retention agreements with vendors prevent your IP from becoming training data. Code review requirements ensure AI-generated code gets human scrutiny before deployment. Opt-in consent mechanisms address privacy concerns for recording tools. An approved vendor list streamlines procurement while ensuring security review. Data retention policies limit your exposure window. License scanning for AI-generated code catches potential open-source compliance issues.

    Quadrant 3: Medium Value, Low Risk (Govern Lightly)

    Helpful use cases with limited downside. Don’t over-engineer governance here—you’ll slow down innovation without meaningful risk reduction. Internal knowledge assistants, content drafting tools, and research summarization fit this profile.

    The primary concerns are accuracy-related: hallucinations and inaccurate information, stale information in knowledge bases, and gaps in source attribution. These can cause problems, but they’re unlikely to trigger regulatory action or make headlines. The appropriate response is light-touch governance: basic logging for troubleshooting, user feedback loops to catch quality issues, source citation requirements to enable verification, and regular accuracy spot-checks to ensure the system remains reliable.

    Quadrant 4: Low Value, High Risk (Reconsider)

    Why take significant risk for marginal value? This quadrant should give you pause. AI-generated customer communications without review, automated decision-making in regulated domains without oversight, and unsupervised agents with broad system access all fall here. The recommendation is clear: either add human oversight to move these use cases into Quadrant 2, or defer them until your governance capability matures. Some risks simply aren’t worth taking for limited business benefit.

    Building Your Risk Assessment Process

    Creating a risk heatmap isn’t a one-time exercise—it’s an ongoing practice. Here’s how to build a systematic approach that scales as your AI usage grows.

    Start by inventorying your AI use cases. Create a complete list of AI tools and agents in use—including shadow AI that employees may be using without approval. Gartner research indicates that 81% of organizations are now on their GenAI adoption journey, but many lack visibility into the full scope of AI tools their employees actually use. Your inventory should capture not just sanctioned tools, but the unsanctioned ones that represent hidden risk.

    Next, assess business value for each use case. Consider revenue impact (direct or indirect), efficiency gains, strategic importance, and user adoption and satisfaction. Be honest about which tools are actually driving value versus which are just interesting experiments.

    Then assess risk sensitivity. Evaluate the data types involved (PII, financial, health, legal), regulatory exposure (GDPR, CCPA, HIPAA, SOX), potential for customer harm, reputational risk, and operational criticality. A tool that processes health data carries different risk than one that summarizes internal documents.

    Plot each use case on the heatmap and prioritize accordingly. Governance investment should flow to the high-value, high-risk quadrant first—that’s where incidents occur and where governance creates the most value. Finally, match controls to risk: heavy controls for high-risk use cases, light touch for low-risk ones. The goal isn’t maximum security; it’s appropriate security.

    Common Governance Controls

    Control Purpose When to Apply
    Centralized logging Audit trail for all interactions All use cases
    Agent registry Inventory of deployed agents All use cases
    Role-based access Limit who can use what High-risk use cases
    PII detection/masking Protect personal data Any PII exposure
    Human-in-the-loop Review before action High-stakes decisions
    Kill switch Rapid shutdown capability Autonomous agents
    Prompt injection testing Security validation Customer-facing agents
    Policy enforcement Programmatic guardrails High-risk use cases

    The Governance Spectrum

    Think of governance as a spectrum, not a binary. The NIST AI Risk Management Framework provides a useful structure here, with implementation tiers ranging from basic documentation (Tier 1) to comprehensive automated monitoring and response (Tier 4). Most organizations will have AI use cases at multiple tiers simultaneously—and that’s exactly right.

    Minimal governance—basic logging, user feedback, and periodic review—is appropriate for internal tools and low-risk experiments. Standard governance adds comprehensive logging, access controls, an approved vendor list, and regular audits; this fits production tools and medium-risk use cases. Maximum governance includes all standard controls plus human-in-the-loop review, real-time monitoring, immutable audit logs, regular security testing, and compliance certification. This level is appropriate for customer-facing, regulated, and high-stakes use cases.

    For CISOs developing governance programs, our AI Governance Checklist provides a comprehensive starting point for building these controls into your organization.

    Evolving Your Heatmap

    Your risk profile changes over time. A Gartner survey found that organizations with high AI maturity keep their AI initiatives live for at least three years at rates more than double those of lower-maturity peers—45% versus 20%. One key differentiator is governance that evolves with the technology.

    Plan to reassess when new use cases emerge that require fresh assessment. Maturing use cases may need upgraded controls as they scale from pilot to production. Changing regulations—like the EU AI Act—can shift risk levels overnight. And incident learnings, whether from your own experience or publicized failures at other organizations, should inform control updates.

    Review your heatmap quarterly. What was acceptable at pilot may not be acceptable at scale.

    The Bottom Line

    Risk-proportional governance is about making smart trade-offs. Over-govern and you kill innovation. Under-govern and you create liability. The heatmap helps you find the right balance for each use case.

    The enterprises winning with AI aren’t the ones with the most restrictive policies or the most permissive ones. They’re the ones who’ve figured out how to match governance to risk—protecting what matters while letting innovation flourish where it can.

    Ready to build risk-proportional AI governance? Talk to an expert to see how Olakai helps you assess risk, implement controls, and govern AI responsibly.
  • AI Governance Checklist for CISOs

    AI Governance Checklist for CISOs

    AI is no longer an IT experiment—it’s an enterprise reality. Your employees are using AI tools (sanctioned or not), your vendors are embedding AI into their products, and your board is asking about AI strategy.

    For CISOs, this creates a challenge with no easy answers: How do you govern AI without blocking innovation? How do you protect data without slowing business? How do you maintain compliance when the technology moves faster than regulations?

    The stakes are high. According to the 2025 CSA AI Security Report, only about a quarter of organizations have comprehensive AI security governance in place—the remainder rely on partial guidelines or policies still under development. Meanwhile, 100% of organizations plan to incorporate generative AI, and Gartner predicts over 100 million employees will interact with AI by 2026. The gap between AI adoption and AI governance represents real risk.

    This checklist provides a structured framework for evaluating and improving your organization’s AI governance maturity.

    How to Use This Checklist

    For each question, score your organization from 0 (not in place—no capability or process exists), to 1 (partial—some capability exists but gaps remain), to 2 (mature—fully implemented and operational). Add scores within each category to identify strengths and weaknesses.

    Category 1: Visibility

    Can you see what AI is doing in your organization?

    Audit and Logging: Can we audit every agent decision? Do we have centralized logging for all AI interactions, including inputs, outputs, and decisions made? The ability to answer “what did this system do and why” is foundational to everything else in governance.

    Complete inventory: Do we have a complete inventory of all AI agents and tools in use—including shadow AI that employees may be using without approval? According to research, 78% of CISOs believe AI is affecting cybersecurity, but 45% admit they’re still not ready to address the problem. You can’t govern what you can’t see.

    Data lineage: Can we trace data lineage for any agent interaction? Do we know what data sources each agent accessed and what data it produced? This becomes critical during incidents and audits.

    Sensitive data access: Do we know which agents access sensitive data sources? Is there a registry mapping agents to the data they can access? Sensitive data exposure ranks as the leading AI security concern among survey respondents.

    Shadow AI detection: Can we detect shadow AI usage—unapproved tools that employees are using? Do we monitor for this actively? Given that most organizations lack formal AI risk management programs, shadow AI often operates completely below radar.

    Category 1 Score: ___ / 10

    Category 2: Control

    Can you control what AI does and who can change it?

    Deployment authority: Who can deploy agents? Who can change their prompts? Is there clear ownership and authorization for AI deployments? Without clear authority, agents proliferate without oversight.

    Role-based access: Do we have role-based access control (RBAC) for agent capabilities? Can we limit what different agents can do based on sensitivity? Not every agent needs access to every system.

    Approval workflows: Is there an approval process for new agents entering production? Do security, legal, and compliance review before deployment? The SANS report highlights a concerning lack of security team involvement in governing GenAI—many believe they should play a role but few organizations have formal processes.

    Policy enforcement: Can we enforce policies programmatically—not just through guidelines? Are guardrails built into the infrastructure? Policies that rely solely on human compliance will fail.

    Security testing: Do we test agents for security vulnerabilities before deployment? Do we check for prompt injection, jailbreaking, and data leakage risks? According to research, 62% of AI-generated code is either incorrect or contains a security vulnerability.

    Category 2 Score: ___ / 10

    Category 3: Data

    Is sensitive data protected when AI accesses it?

    Data source mapping: Which data sources can each agent access? Is there a clear registry of permissions and restrictions? Data access should be explicit, not assumed.

    PII protection: Do we have PII detection and masking in place? Can we prevent agents from exposing personally identifiable information? This is table stakes for any customer-facing AI.

    Regulatory compliance: Are we compliant with GDPR, CCPA, and other data regulations for AI-processed data? Have we verified this with legal? As of mid-2025, state legislatures had introduced some 260 AI-related bills during the 2025 legislative sessions—the regulatory landscape is rapidly evolving.

    Data retention: Do we have data retention policies for agent interactions? Do we know how long logs are kept and when they’re deleted? Compliance requirements vary by jurisdiction and data type.

    Right to deletion: Can we fully delete user data on request (right to be forgotten)? Does this include data in AI training sets and logs? This is a legal requirement in many jurisdictions and technically complex to implement.

    Category 3 Score: ___ / 10

    Category 4: Incident Response

    Can you respond when something goes wrong?

    Rollback capability: How do we roll back a rogue or compromised agent? Can we quickly revert to a previous version or disable an agent entirely? The faster you can respond, the smaller the impact.

    Incident runbooks: Do we have runbooks for common AI incidents—data leaks, hallucinations, prompt injection attacks, model compromise? AI introduces failure modes that traditional security runbooks don’t cover.

    Kill switch: Can we disable an agent in less than 5 minutes? Is this tested regularly? When an agent is causing harm, every minute matters.

    On-call ownership: Who is on-call for AI security incidents? Is there a clear escalation path and 24/7 coverage? AI systems don’t fail during business hours only.

    Post-mortems: Do we conduct post-mortems and share learnings after AI incidents? Is there a continuous improvement process? Learning from incidents prevents repetition.

    Category 4 Score: ___ / 10

    Category 5: Compliance and Audit

    Can you prove compliance to auditors and regulators?

    Audit readiness: Can we pass an AI audit today? If regulators asked to see our AI governance, could we demonstrate compliance? The CSA AI Controls Matrix provides 243 control objectives across 18 security domains—a useful benchmark.

    Immutable logs: Do we have immutable logs for sensitive operations? Can we prove logs haven’t been tampered with? Immutability is critical for legal and regulatory purposes.

    Policy documentation: Are AI governance policies documented and communicated? Do employees know what’s expected? Documentation is the foundation of demonstrable compliance.

    Compliance metrics: Do we measure and report Governance Compliance Rate? Can we show the percentage of AI interactions that comply with policies? Metrics make governance tangible.

    Board visibility: Is AI governance represented at the board level? Do executives understand AI risk exposure? AI risk is business risk and belongs in board conversations.

    Category 5 Score: ___ / 10

    Scoring Interpretation

    Total Score Maturity Level Recommended Action
    0-10 Foundational Start with visibility: establish inventory and basic logging before adding controls
    11-25 Developing Fill critical gaps: prioritize based on risk—data protection and incident response are typically highest priority
    26-40 Established Optimize and scale: strengthen existing capabilities and prepare for audit
    41-50 Advanced Lead: share practices, influence industry standards, and continue innovation

    Priority Actions by Risk Level

    If you’re processing customer PII: Prioritize PII detection and masking, comprehensive logging, RBAC, right to deletion capability, and regulatory compliance verification. Data protection failures have immediate regulatory and reputational consequences.

    If you’re in a regulated industry: Prioritize immutable audit logs, policy documentation, compliance metrics, approval workflows, and audit readiness. Key compliance pathways include mappings to the EU AI Act, NIST AI 600-1, ISO 42001, and BSI AIC4 Catalogue.

    If you’re scaling AI rapidly: Prioritize complete inventory, shadow AI detection, programmatic policy enforcement, kill switch capability, and incident runbooks. Speed without governance creates technical and compliance debt.

    If you’re just starting: Prioritize basic logging, agent inventory, clear ownership, simple approval process, and documentation. Foundation comes before sophistication.

    The AI Risk Heatmap

    Not all AI use cases carry equal risk. Prioritize governance based on both business value and risk sensitivity—a concept we explore in depth in our AI risk heatmap framework.

    High Value, High Risk (Govern Tightly): Customer support agents with PII access, financial data analysis agents, contract review and drafting, and HR policy chatbots need RBAC, PII protection, comprehensive logging, human-in-the-loop review, and regular audits.

    High Value, Medium Risk (Govern Moderately): Code assistants and copilots, sales research assistants, and AI meeting note takers need zero data retention agreements, code review requirements, consent mechanisms, and approved vendor lists.

    Medium Value, Low Risk (Govern Lightly): Internal knowledge assistants and content drafting tools need basic logging, user feedback loops, and source citation requirements.

    Getting Started

    If you scored below 25, focus on these immediate actions.

    First, conduct an AI inventory. Survey departments, review expense reports, analyze network traffic. You can’t govern what you can’t see, and the gap between what security teams believe is deployed and what’s actually in use is often substantial.

    Second, establish basic logging. Ensure all production AI agents have logging enabled. Centralize logs where possible. This creates the audit trail everything else depends on.

    Third, define ownership. Assign clear owners for AI governance. Create an AI governance committee if needed. Without ownership, governance becomes everyone’s problem and no one’s priority.

    Fourth, document policies. Write down acceptable use guidelines. Communicate them to all employees. Documentation transforms implicit expectations into enforceable standards.

    Fifth, plan for incidents. Create basic runbooks for data leaks, hallucinations, and unauthorized access. Incident response planned in advance is dramatically more effective than improvisation under pressure.

    For measuring the business impact of your governance investments, see our AI ROI measurement framework.

    The Bottom Line

    AI governance isn’t about blocking innovation—it’s about enabling it responsibly. The organizations that build strong governance foundations now will scale AI with confidence, while others will hit walls of compliance violations, security incidents, and audit failures.

    This checklist is a starting point. The goal isn’t perfection; it’s continuous improvement toward a governance posture that matches your AI ambitions. The Future of Agentic guide to agent characteristics provides additional context on what makes AI systems increasingly autonomous—and why governance becomes more critical as autonomy increases.

    Ready to improve your AI governance maturity? Talk to an expert to see how Olakai provides the visibility, controls, and compliance tools CISOs need.

  • Shadow AI: The Hidden Risk in Your Enterprise

    Shadow AI: The Hidden Risk in Your Enterprise

    Your employees are using AI tools you don’t know about. Right now. They’re pasting customer data into ChatGPT to draft emails. They’re uploading financial documents to AI summarizers. They’re using unapproved coding assistants that send your source code to third-party servers.

    And the numbers are staggering. According to a Gartner survey of cybersecurity leaders conducted in 2025, 69% of organizations suspect or have evidence that employees are using prohibited public GenAI tools. Microsoft’s research found that 71% of UK employees admitted to using unapproved AI tools at work—with 51% doing so at least once a week. This isn’t occasional experimentation; it’s a systematic shadow operation running parallel to your official technology stack.

    This is shadow AI—the enterprise AI equivalent of shadow IT—and it represents one of the most significant and underestimated risks facing organizations today.

    What is Shadow AI?

    Shadow AI refers to AI tools and services that exist outside your organization’s visibility and governance. They’re not approved by IT, security, or compliance teams. They’re not visible in your technology inventory. They’re not governed by your data protection policies. And they’re not monitored for security, compliance, or cost implications.

    Just as shadow IT emerged when employees started using Dropbox, Slack, and other cloud tools without IT approval, shadow AI is spreading as employees discover that AI makes their jobs easier—regardless of whether it’s sanctioned. According to the 2025 State of Shadow AI Report, the average enterprise hosts 1,200 unauthorized applications, and 86% of organizations are blind to AI data flows. Nearly half (47%) of people using generative AI platforms do so through personal accounts that companies aren’t overseeing.

    Why Shadow AI is Different from Shadow IT

    Shadow AI carries risks that go beyond traditional shadow IT in fundamental ways.

    Data goes out, not just in. When an employee uses unauthorized Dropbox, they might store company files externally—a risk, but a bounded one. When they use unauthorized AI, they actively send sensitive data to third-party models. That customer complaint they pasted into ChatGPT? It might be used to train the model, potentially surfacing in responses to competitors. According to Cisco’s 2025 study, 46% of organizations reported internal data leaks through generative AI—data that flowed out through employee prompts rather than traditional exfiltration.

    Prompts reveal more than files. The questions employees ask AI reveal context that raw data doesn’t. “Summarize this contract and identify terms unfavorable to us” tells the AI (and its operator) not just the contract contents, but your negotiating strategy and concerns. The prompt itself is intelligence.

    Answers drive decisions. When AI provides analysis or recommendations, employees act on them. An unauthorized AI tool giving bad financial advice, incorrect legal interpretation, or flawed technical guidance can lead to costly mistakes with no audit trail. And there’s no recourse when things go wrong.

    The attack surface is enormous. Prompt injection, jailbreaking, and other AI-specific attacks create new vectors. An employee who pastes customer data into a compromised AI tool might unknowingly expose that data to attackers who’ve manipulated the model.

    The Scope of the Problem

    If you think shadow AI isn’t happening in your organization, the statistics suggest otherwise. Gartner predicts that by 2030, more than 40% of enterprises will experience security or compliance incidents linked to unauthorized shadow AI. That’s not a distant future risk—it’s the trajectory we’re already on.

    The financial impact is real and immediate. According to IBM’s 2025 Cost of Data Breach Report, shadow AI incidents now account for 20% of all breaches and carry a cost premium: $4.63 million versus $3.96 million for standard breaches. AI-associated cases caused organizations more than $650,000 extra per breach. The gap between AI adoption and AI governance is where shadow AI thrives—and where the costs accumulate.

    Perhaps most concerning: 83% of organizations operate without basic controls to prevent data exposure to AI tools. The average company experiences 223 incidents per month of users sending sensitive data to AI applications—double the rate from a year ago. And 27% of organizations report that over 30% of their AI-processed data contains private information, including customer records, financial data, and trade secrets.

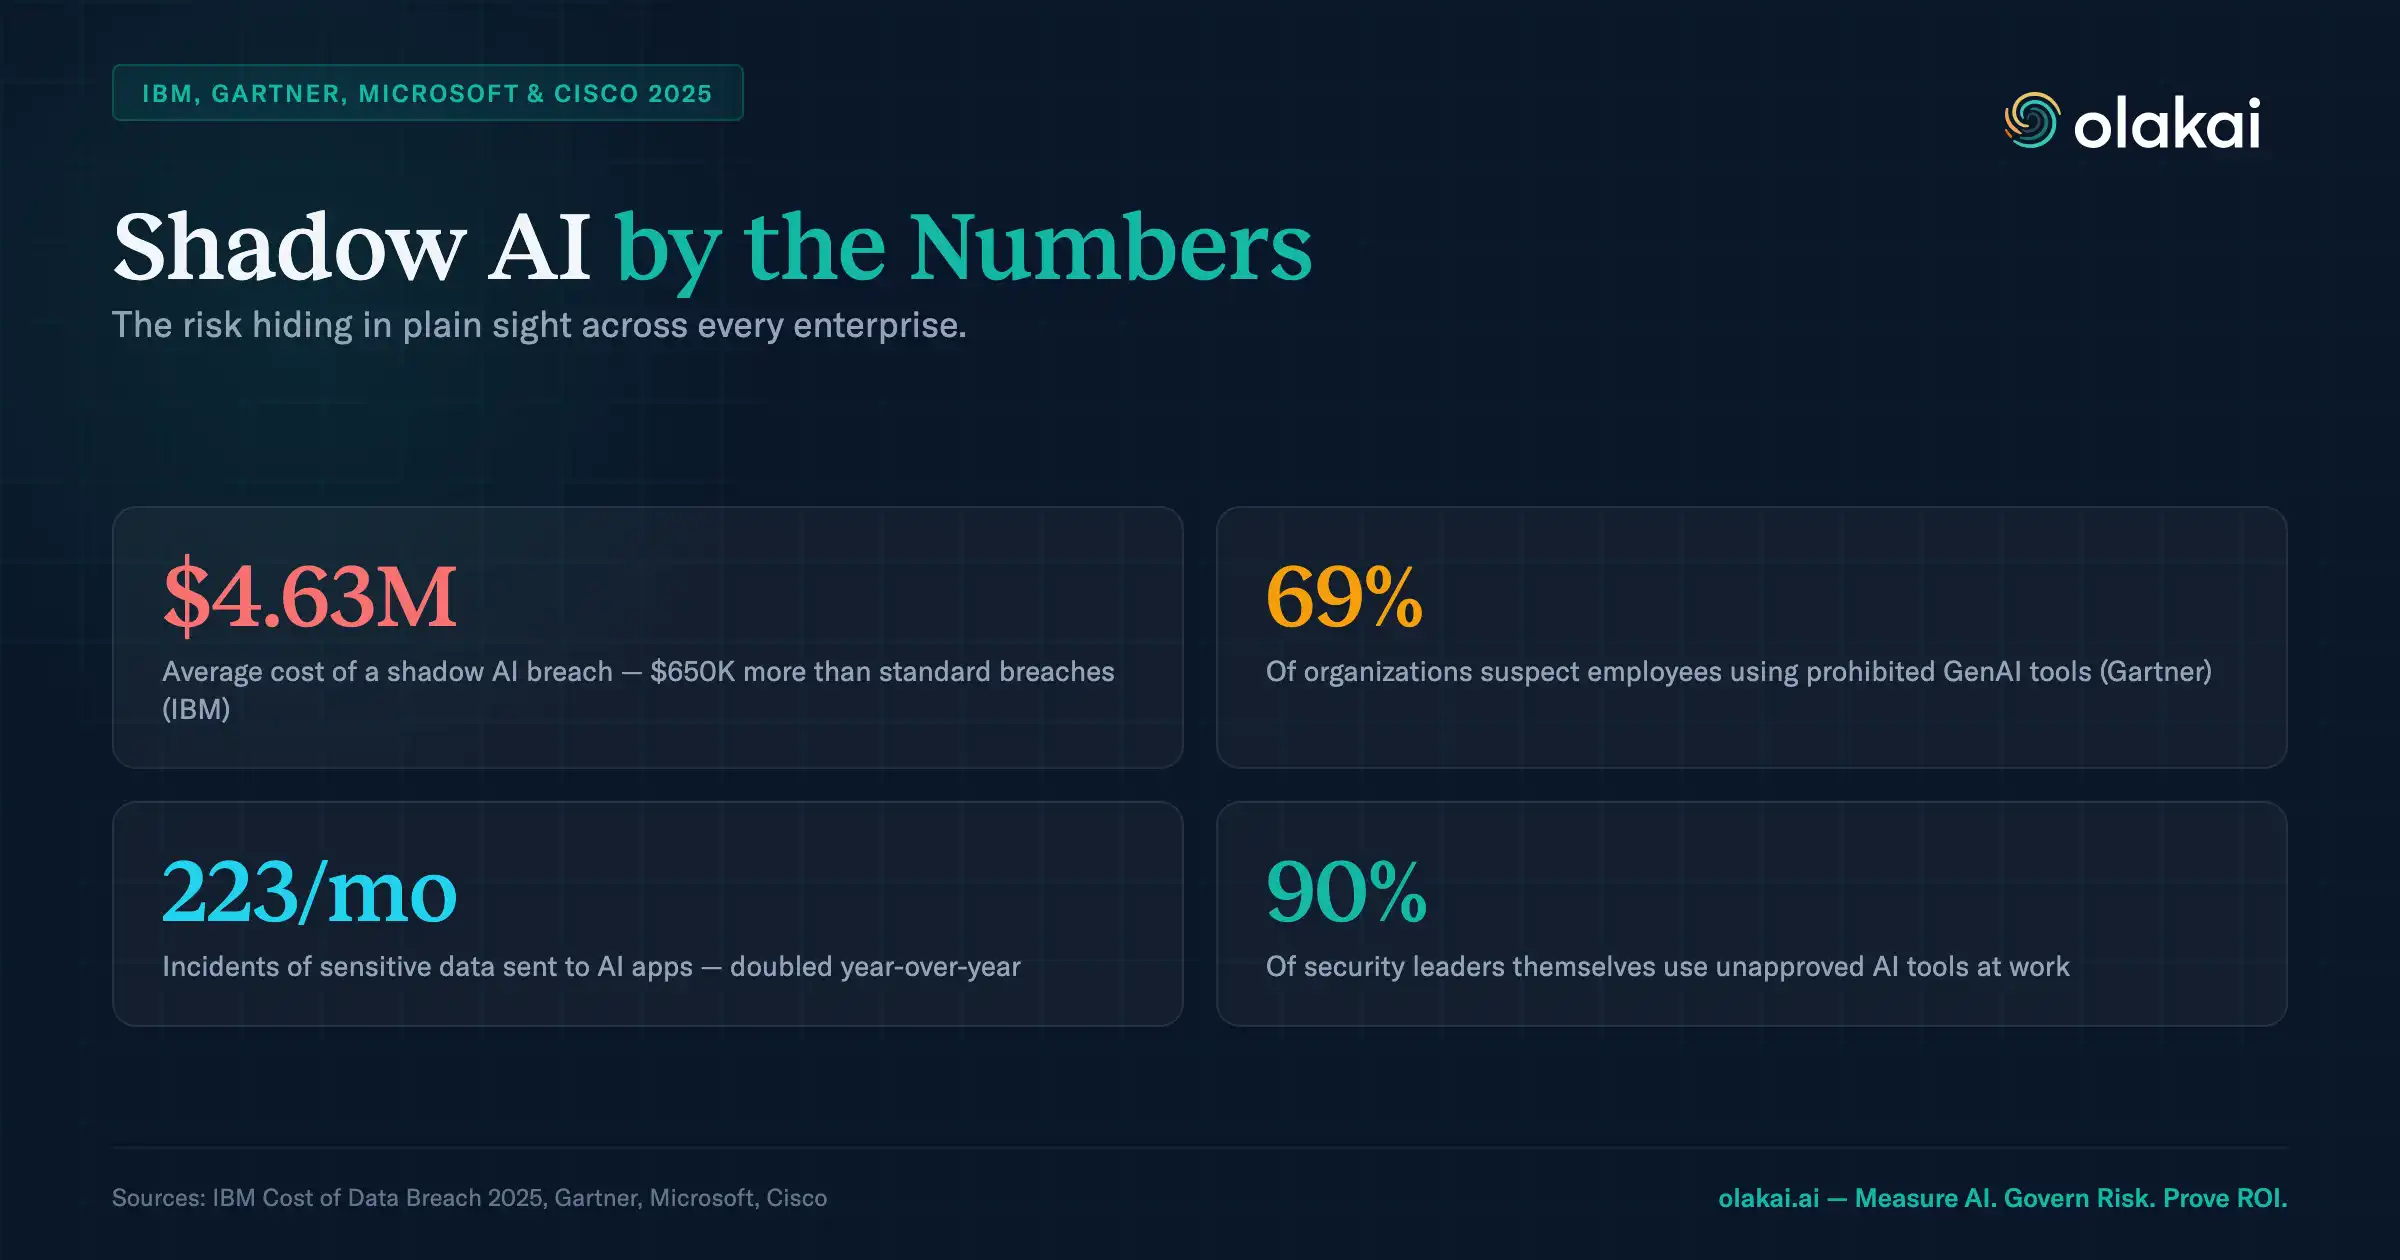
    Shadow AI by the Numbers — $4.63M breach cost, 69% suspect prohibited use, 223 incidents per month, 90% of security leaders use unapproved tools

    Common Shadow AI Scenarios

    These aren’t hypothetical risks. They’re happening in organizations like yours, every day.

    The helpful marketer uses an AI writing tool to draft blog posts. She pastes competitor analysis, product roadmaps, and customer testimonials as context. The tool’s terms of service allow training on user inputs. Your competitive intelligence is now potentially in someone else’s model—or in their training data, waiting to surface in responses to your competitors.

    The efficient developer uses an unapproved coding assistant to speed up development. He pastes internal API documentation and proprietary algorithms for context. The code generated might include those patterns in ways that constitute IP leakage, and the original code may be used for model training.

    The overwhelmed HR manager uses an AI tool to help screen resumes and draft interview questions. She pastes candidate information, salary data, and performance review excerpts. She’s now exposed PII to an unapproved processor, potentially violating GDPR and internal policies—with no documentation of consent or processing basis.

    The pressured analyst uses an AI tool to summarize earnings calls and model scenarios. He pastes material non-public information into prompts. If that information surfaces elsewhere—or even if someone later discovers it was processed through an unauthorized channel—it could trigger SEC scrutiny.

    Why Traditional Controls Don’t Work

    The approaches that worked for shadow IT often fail for shadow AI.

    Blocking doesn’t scale. You can’t block every AI tool—new ones appear daily. Employees use personal devices. VPNs and proxies circumvent network controls. Small businesses face the highest risk, with 27% of employees in companies with 11-50 workers using unsanctioned tools. These organizations average 269 shadow AI tools per 1,000 employees while lacking the security resources to monitor them.

    Policies aren’t enough. Acceptable use policies help, but they rely on employees reading, understanding, and following them. When AI makes someone dramatically more productive, policy compliance becomes an afterthought. According to research, 90% of security leaders themselves report using unapproved AI tools at work—with 69% of CISOs incorporating them into daily workflows. If the people writing the policies aren’t following them, you have a systemic problem.

    Training has limits. Security awareness training can highlight risks, but it can’t prevent every incident. Employees under deadline pressure make expedient choices.

    A Better Approach: Discovery, Governance, and Alternatives

    Effective shadow AI management requires a multi-pronged approach that acknowledges human nature while protecting organizational interests.

    Discovery: See what’s happening. You can’t govern what you can’t see. Modern shadow AI discovery involves monitoring network traffic for AI tool usage patterns, analyzing browser extensions and desktop applications, surveying employees about tools they’re using, and reviewing expense reports and credit card statements for AI subscriptions. The goal isn’t surveillance—it’s visibility. You need to know what’s being used so you can make informed governance decisions.

    Risk assessment: Prioritize what matters. Not all shadow AI carries equal risk. Assess each discovered tool against data sensitivity (what data types are being processed?), regulatory exposure (does usage implicate GDPR, CCPA, HIPAA, or SOX?), vendor risk (what are the tool’s data handling practices?), and business impact (how critical is this tool to the workflow?). For a framework on matching governance to risk levels, see our AI risk heatmap approach.

    Provide sanctioned alternatives. Heavy-handed blocking drives shadow AI underground. Instead, provide approved alternatives that meet employee needs: deploy enterprise AI tools with proper data protection, negotiate data processing agreements with AI vendors, configure guardrails like PII detection and content filtering, and communicate what’s available and how to access it. When approved tools are easy to use and meet employee needs, shadow AI becomes less attractive.

    Continuous monitoring. Shadow AI isn’t a one-time problem to solve—it’s an ongoing challenge to manage. Establish regular discovery scans to identify new tools, usage monitoring for sanctioned tools, incident response procedures for policy violations, and feedback loops to understand why employees seek alternatives. According to Delinea’s 2025 report, 44% of organizations with AI usage struggle with business units deploying AI solutions without involving IT and security teams. That gap needs ongoing attention.

    The Role of Governance

    Ultimately, shadow AI is a symptom of governance gaps. Organizations that struggle with shadow AI often lack visibility (no central inventory of AI tools and usage), policy (no clear guidelines on acceptable AI use), process (no fast-track approval for low-risk AI tools), alternatives (no sanctioned tools that meet employee needs), and culture (no psychological safety to ask “Can I use this?”).

    Building AI governance isn’t about creating barriers—it’s about creating clarity. Employees want to do the right thing. They just need to know what the right thing is. Our CISO governance checklist provides a comprehensive framework for building these foundations.

    Getting Started

    If you’re concerned about shadow AI in your organization—and if you’re paying attention to the statistics, you should be—start with a discovery exercise. Survey employees, analyze network traffic, review expense reports. Understand your current exposure before trying to solve it.

    Assess risks by prioritizing discovered tools by data sensitivity and regulatory exposure. Focus governance efforts on highest-risk usage first—you can’t solve everything at once.

    Provide alternatives by deploying sanctioned AI tools that meet legitimate employee needs. Make approved tools easier to use than shadow alternatives. If the official path is harder than the unofficial one, you’ll keep losing.

    Build governance foundations through policies, processes, and monitoring. But start lightweight—you can add sophistication over time. Gartner also predicts that by 2030, 50% of enterprises will face delayed AI upgrades and rising maintenance costs due to unmanaged GenAI technical debt. Building governance now prevents that debt from accumulating.

    Communicate clearly. Tell employees what’s approved, what’s not, and why. Create a safe channel to ask questions. The Future of Agentic use case library can help illustrate what good AI governance looks like in practice.

    The Bottom Line

    Shadow AI is already in your organization. The question isn’t whether it exists, but how you’ll respond. A heavy-handed approach drives usage underground. A permissive approach exposes you to risk. The right approach—discovery, governance, and alternatives—lets you get the benefits of AI while managing the downsides.

    Want to understand your shadow AI exposure? Talk to an expert to see how Olakai helps enterprises discover, assess, and govern AI usage across the organization.